Skip to content

Public technology that complies, protects and can be audited.

Portals, systems and digital security for public institutions, with verifiable evidence in every delivery.

What we solve

Each regulation is a sheet in the file: what it requires, where institutions usually fall short and what we deliver.

FILE LS-TRANSPARENCIA-01Sheet 1/5

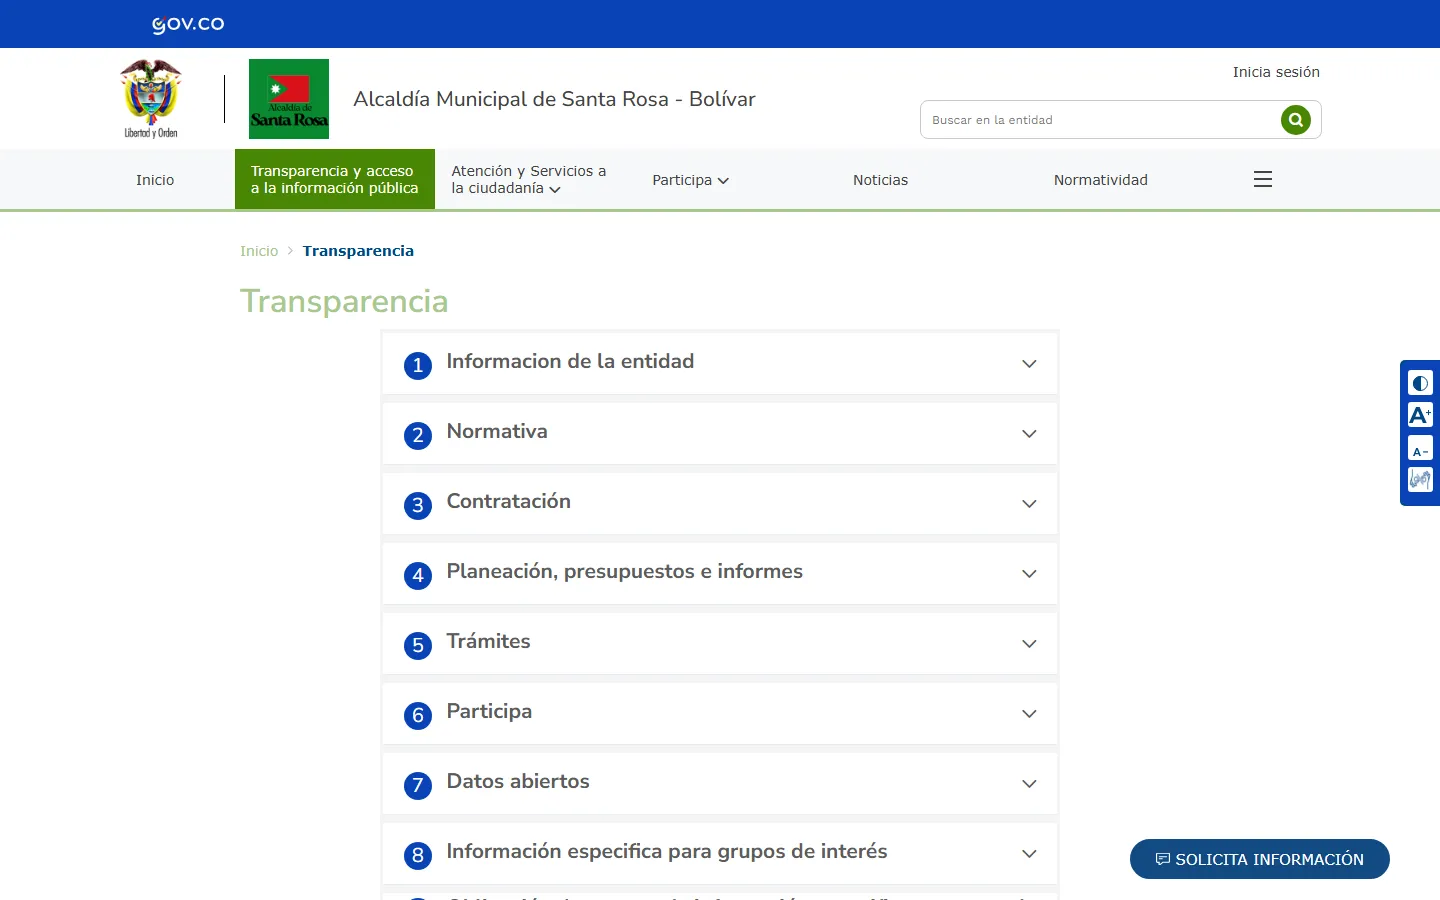
Transparency and ITA compliance

We organize the information required by Colombia's Law 1712 of 2014 and prepare institutions for the Inspector General's Transparency and Access to Information Index (ITA).

What it sets out

  • Publish the minimum mandatory categories of information required by Law 1712 of 2014.
  • Complete the compliance matrix in the Procuraduría's ITA application.
  • Keep information current and easy to find.

Common gaps

  • Documents published outside the Transparency menu.
  • Broken links and outdated files.
  • Categories that exist in name only, with no content.

What we deliver

  • Requirement-by-requirement PRE baseline with evidence.
  • Prioritized improvement plan.
  • Restructured Transparency menu.
  • POST measurement with the same requirement catalog.
FILE LS-ACCESIBILIDAD-02Sheet 2/5

Accessible portals

We design and fix portals to meet the web accessibility guidelines of MinTIC Resolution 1519 of 2020 (WCAG 2.1, level AA).

What it sets out

  • Meet level AA of the Web Content Accessibility Guidelines (WCAG) 2.1.
  • Apply it to portal updates, redesigns and existing content.

Common gaps

  • Images without alternative text.
  • Insufficient contrast between text and background.
  • Forms that cannot be used with a keyboard.
  • Scanned PDF documents with no text.

What we deliver

  • Automated and manual accessibility audit.
  • Fixes to templates and components.
  • Accessible publishing guide for the communications team.
  • Accessibility statement.
FILE LS-SEGURIDAD-03Sheet 3/5

Digital security and MSPI

We help institutions meet the digital security obligations of Colombia's Digital Government Policy (Decree 767 of 2022) and MinTIC's Information Security and Privacy Model.

What it sets out

  • Ensure digital security and data protection when delivering services.
  • Prevent risks and ensure continuity in the face of incidents.
  • Implement the Information Security and Privacy Model (MSPI).
  • Apply the website digital security measures in Annex 3 of Resolution 1519 of 2020.

Common gaps

  • Outdated servers and content management systems.
  • Missing security headers on the portal.
  • No asset inventory or incident response plan.

What we deliver

  • Exposed surface assessment.
  • Portal and server hardening.
  • Inputs for the MSPI (assets, risks and controls).
  • Incident response procedure.
FILE LS-GESTION-04Sheet 4/5

Management systems and citizen requests

We build systems to register, assign and answer citizen requests within legal deadlines, and internal project tracking tools.

What it sets out

  • Resolve petitions within fifteen (15) days of receipt, unless a special legal rule applies.
  • Let anyone submit petitions free of charge.

Common gaps

  • Requests arriving through several channels with no single tracking number.
  • No alerts before deadlines expire.
  • Request reports assembled by hand.

What we deliver

  • Request module with tracking numbers, assignment and alerts.
  • Deadline tracking dashboard.
  • Project and risk tracking for managers.
  • Staff training.
FILE LS-IA-05Sheet 5/5

AI for public institutions

We put Colombia's National AI Policy (CONPES 4144 of 2025) into practice with scoped, supervised and measurable projects.

What it sets out

  • Promotes the adoption of AI systems in public institutions and regions, with actions through 2030.

Common gaps

  • Pilots without a measurable goal.
  • AI tools used without rules on personal data.
  • Automated answers with no human review.

What we deliver

  • Selection of use cases with a clear return.
  • Service assistants and request classification with human approval.
  • Data handling rules and a decision log.
  • Before-and-after measurement.

How we measure compliance

A traceable method: we measure first, fix, and measure again with the same requirement catalog.

  1. Step 01

    PRE baseline

    Official matrix requirement by requirement and a crawl of the portal, with dated evidence.

  2. Step 02

    Improvement plan

    Prioritized findings with owners and dates.

  3. Step 03

    Fixes

    Changes to the portal, the Transparency menu and the content.

  4. Step 04

    POST measurement

    The same requirement catalog, compared requirement by requirement.

Who we serve

To: Public institutions

Public institutions

Municipal and departmental governments, public companies, public hospitals and national agencies that must comply with Law 1712, Resolution 1519 and MSPI without audit findings.

To: Integrators and prime contractors

Integrators and prime contractors

Firms that win public contracts and need a technical partner who delivers with confidentiality, documentation and clear deliverables.

Public sector work

Capability statement

Capabilities, experience and working model in a document built for evaluators and integrators.

See the capability statement